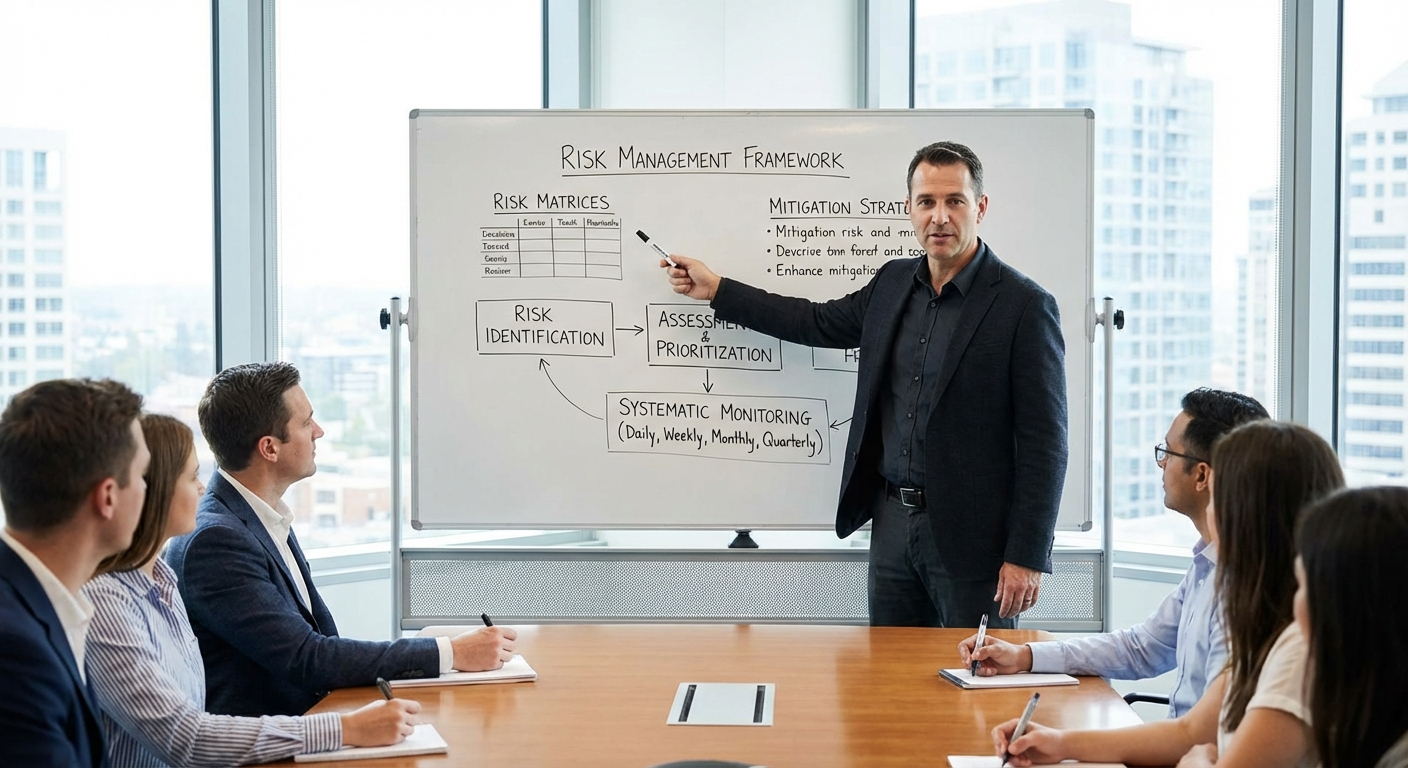
Risk management has been a core requirement of ISO 9001 since the 2015 revision, yet most plants still treat it as a documentation exercise. They produce a risk register at certification time, file it, and never look at it again until the auditor returns. That approach actively damages quality performance because it disconnects risk identification from the daily decisions that actually prevent defects.
Real risk management is a operational discipline, not a paperwork ritual. It means building a structured process for finding what can go wrong, ranking those threats by severity and likelihood, and applying concrete mitigation actions with named owners and deadlines. When this works, you catch process failures before they become scrap, customer escapes, or audit nonconformities.
I have audited plants that maintained immaculate risk registers alongside double-digit scrap rates. The register existed, but nobody used it to drive action. The standard is clear: Clause 6.1 requires organisations to determine risks and opportunities, and Clause 9.3 requires management review to evaluate their effectiveness. The gap is always in execution, not in the existence of a document.
Risk Identification: Building a Real Process, Not a Brainstorm
Start with your existing quality data, not with a brainstorming session. Your nonconformance reports, 8D corrective actions, customer complaints, internal audit findings, and supplier scorecards already contain every significant risk your plant faces. The job is to extract and structure that information systematically. A risk identified from historical defect data is infinitely more valuable than a hypothetical one guessed at in a meeting room.
Layer that historical data with structured process analysis. For manufacturing, PFMEA is your primary tool: it forces you to break each process step into potential failure modes, their effects, and their causes. For design, DFMEA does the same. Both feed directly into your control plan, which is where risk mitigation actually meets production. If your PFMEA is sitting in a file and your control plan does not reference its outputs, your risk identification is disconnected from your process control.
Cast the net wider than just production. Review your supply chain for single-source vulnerabilities, your equipment for critical-to-quality assets with no redundancy, and your workforce for key-person dependencies in inspection or setup roles. Regulatory changes, such as new REACH restrictions or updated IATF 16949 sanctioned interpretations, also belong on the register. The goal is a living document, not a static snapshot.
Document each identified risk with a consistent structure: the process or area affected, the specific failure mode, the potential consequence, and the current detection method. This structure matters because it determines whether your mitigation actions will target the cause, the effect, or the detection gap. Without that clarity, teams waste resources addressing symptoms instead of root causes.
Assessment and Prioritisation: Scoring What Actually Matters
Not every risk deserves equal attention. A 5×5 risk matrix is the standard tool for prioritisation because it forces discipline: you rate severity on a 1-5 scale and likelihood on a 1-5 scale, then multiply. A severity-5 event is one that causes customer injury, a regulatory breach, or a line-down situation. A severity-1 event is a minor internal inconvenience. Be honest with the scoring — inflating every risk to a 5 makes the matrix useless.
If you operate under IATF 16949, PFMEA scoring uses the more granular 1-10 scale for severity, occurrence, and detection, producing an RPN or, under the newer AIAG-VDA harmonisation, an Action Priority of High, Medium, or Low. Use whichever your customer base requires, but apply it consistently. The danger is always the same: teams scoring detection favourably because a control exists on paper, even when that control is unreliable in practice.
Prioritisation must account for detection capability, not just severity and likelihood. A low-frequency, high-severity risk with poor detection is more dangerous than a moderate risk you catch at first-piece inspection. This is why MSA studies matter: if your gauge R&R is above 30 percent, your detection score should reflect that weakness. You cannot claim a risk is controlled if the measurement system itself is a source of variation.
Review the prioritised list with cross-functional input. Production supervisors see constraints that engineers miss. Operators know which checks are routinely skipped under time pressure. Quality engineers understand the statistical risk of process drift. The prioritisation meeting should be short, evidence-based, and conclude with a ranked list that directs resources to where they reduce risk most effectively.
Mitigation Strategy: Selecting the Right Response
Risk Response Selection
Reactive habits
- Add inspection at end of line
- Write a new work instruction
- Retrain operators after defects occur
- Log the risk and revisit next year
Effective mitigation
- Eliminate the failure mode through design change
- Engineer poka-yoke into the process
- Transfer risk via contract or insurance
- Accept only with documented justification and monitoring
The four standard mitigation responses are avoid, reduce, transfer, and accept. Each carries a different cost profile and a different level of process change. Avoidance means engineering the failure mode out entirely — redesigning the part, changing the process sequence, or specifying a different material. This is the most expensive option upfront but often the cheapest over the product lifecycle.
Reduction is the most common response in manufacturing quality: you lower the likelihood or improve the detection through process controls. This is where poka-yoke devices, automated inspection, SPC charting, and tightened Cpk targets live. A reduction strategy must specify the control method, the responsible function, and the validation frequency. A plan that says "monitor process" without defining how, who, and when is not a mitigation.
Transfer means moving the risk to a party better equipped to manage it. In practice, this includes specifying supplier quality requirements in PPAP submissions, purchasing equipment warranties, or carrying product liability insurance. Transfer does not eliminate the risk to your customer — it changes who bears the operational responsibility. Make sure the receiving party actually has the capability, or you have created a new risk.
Acceptance is the legitimate response for low-severity, low-frequency risks where mitigation cost exceeds the expected loss. Document the decision, the rationale, and the monitoring trigger. Acceptance without documentation is simply negligence: if the risk materialises and there is no record of a conscious decision, the audit finding will be inevitable and the quality cost will be borne in scrap and complaint handling.
Integration: Connecting Risk to the Management System
A risk register that lives outside the management system is dead weight. Integration means connecting risk outputs to the processes that drive daily operations. The control plan must reference PFMEA-driven controls. The internal audit schedule must prioritise high-risk processes. The CAPA system must close the loop by updating risk scores when corrective actions are verified effective.
Management review is where integration becomes visible to leadership. Clause 9.3 requires you to review the effectiveness of actions taken to address risks and opportunities. This is not a slide that says "risks are managed." It is a data-driven discussion: which risks decreased in priority, which increased, which materialised, and what actions are in progress. If leadership cannot answer these questions, the risk process has failed regardless of what the register looks like.
A risk register that does not change a single shop-floor behaviour is a compliance document, not a management tool.
Connect risk management to your KPI system. If OEE drops on a critical-to-quality asset, that is a risk indicator. If first-pass yield trends downward on a process with a high RPN, the risk has increased. Build the dashboards that surface these signals in real time, and link them to escalation procedures so that the right people respond before the defect reaches the customer.
Supplier risk deserves its own integration track. PPAP submissions, supplier audit results, and incoming inspection data all feed the supplier risk profile. When a critical supplier's on-time delivery drops or their PPM defect rate rises, the risk register should reflect that change automatically. Too many plants treat supplier risk as a procurement issue and discover too late that it is a quality issue.
Monitoring and Review: Keeping the Register Alive
Risk Review Cadence by Frequency
- 01Daily shift reviewTier 1: operational risks — equipment status, staffing gaps, supplier alerts
- 02Weekly production meetingTier 2: process risks — yield trends, SPC excursions, open nonconformances
- 03Monthly quality reviewTier 3: systemic risks — CAPA effectiveness, audit findings, risk score changes
- 04Quarterly management reviewTier 4: strategic risks — customer requirements, supply chain, regulatory changes
The review cadence must match the risk velocity. Operational risks — equipment downtime, staffing shortages, material shortages — change daily and need a daily review at shift handover. Process risks, such as Cpk drift or rising nonconformance rates, should appear on the weekly production meeting agenda. Strategic risks, including new regulatory requirements or customer-specified changes, belong in the quarterly management review.
Risk scores change. A process that was stable can drift when tooling wears, when a new operator is assigned, or when a supplier changes a sub-tier source without notification. Reviewing the register means actively asking whether the severity, occurrence, or detection ratings are still valid. If a mitigation action has been implemented and verified, the occurrence score should drop. If a near-miss occurred that your detection system missed, the detection score should rise.
Build a simple trigger system for ad-hoc risk reviews. When a new customer complaint is logged, when an internal audit finds a major nonconformity, or when a key performance indicator breaches its control limit, the relevant risk entries should be re-evaluated immediately. Do not wait for the next scheduled review. The trigger system ensures the risk process responds to reality, not to the calendar.
Continuous improvement closes the loop. Every verified CAPA should produce an updated risk score, a revised control plan entry, or a new PFMEA line item. This is how risk management drives the quality system forward: each problem prevented or solved makes the next problem less likely. Over time, the register becomes a record of organisational learning, not just a list of things that might go wrong.